


Top API Design Principles for Building Scalable and Reliable APIs
Software Development Team
Last Updated: Sep 24, 2026 Total Views: 130
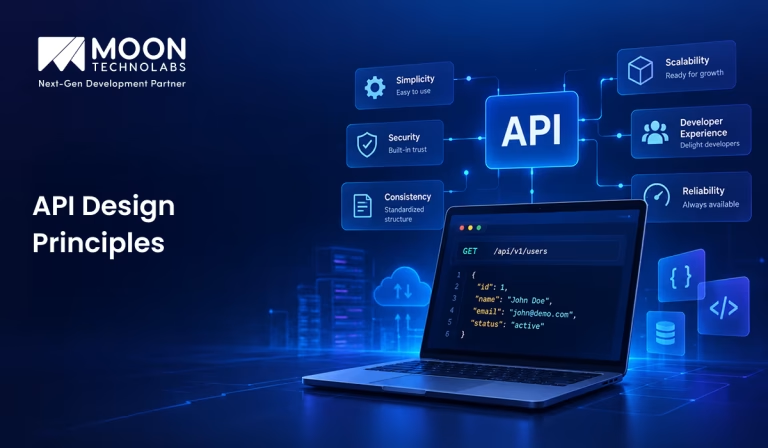
Table of Content


Blog Summary:
Learn the top API design principles for building scalable, reliable, secure, and maintainable APIs. This guide covers essential practices including clear API contracts, versioning, error handling, authentication, rate limiting, caching, and observability. Discover how thoughtful API design can improve performance, simplify maintenance, support future growth, and deliver consistent experiences for applications, developers, and users across evolving software ecosystems.
Table of Content
APIs are the backbone of modern software, connecting applications, services, and platforms at scale. As API traffic and integrations grew, simply making an endpoint functional was no longer enough—APIs needed to be designed for scalability, reliability, security, and long-term maintainability.
Postman’s 2025 State of the API Report, based on responses from more than 5,700 industry professionals, found that 82% of organizations had adopted some level of an API-first approach, highlighting the growing importance of intentional API design.
Reliability is equally critical for applications that depend on consistent service availability. Resilient API architecture helps systems handle failures, increasing traffic, and changing requirements without compromising performance or user experience.
In this guide, we’ll explore the top API design principles, from clear contracts and versioning to error handling, rate limiting, caching, and observability, to help you build APIs that remain scalable, reliable, and easier to maintain as your systems grow.
What are API Design Principles?
API design principles are guidelines helping developers create APIs that are simple, consistent, reliable, and easy to use. They cover areas such as clear naming, predictable request and response formats, proper error handling, security, and consistent use of HTTP methods and status codes.
Good API design also focuses on the developer experience and long-term maintainability. Well-designed APIs are easy to understand, perform efficiently, support backward compatibility, and can evolve without unnecessarily breaking existing applications.
Why are API Design Principles Important?
API design principles establish a common language and structure across endpoints, making them intuitive and predictable. When an API follows clear standards, developers can learn its patterns faster, reduce integration errors, and spend less time deciphering documentation.
As software systems grow, well-designed APIs provide the flexibility needed to evolve without breaking existing clients. By adhering to principles like loose coupling and thoughtful versioning, teams can update underlying architectures, optimize performance, and add new features seamlessly.
Standardized design patterns naturally incorporate robust error handling, proper authentication practices, and consistent data validation. This minimizes security vulnerabilities, ensures predictable behavior under heavy loads, and builds trust between service providers and consumers.
Build High-Performance APIs That Scale With Your Business
Partner with our developers to eliminate bottlenecks, secure your endpoints, and build a robust infrastructure designed for massive enterprise growth.
Top API Design Principles for Building Better APIs
A well-designed API should be easy to understand, secure, reliable, and flexible enough to support future growth. Following established API design principles helps developers create consistent interfaces that simplify integration, improve performance, and make applications easier to maintain:
Design APIs Around Resources
Use Clear Resource Naming
APIs should represent business entities as resources with clear, meaningful names. Resource names should be easy to understand and consistent throughout the API. For example, /users, /products, and /orders clearly communicate what each endpoint represents.
Use Nouns Instead of Verbs
Use nouns to represent resources rather than action-based words. HTTP methods already describe the operation, so endpoints like/users or /orders are generally clearer than /getUsers or /createOrder.
Example:
GET /users
GET /products
GET /orders
This approach keeps endpoint structures predictable and easier for developers to work with.
Use HTTP Methods Correctly
HTTP methods communicate the intended action for a request. Using them consistently makes APIs more intuitive and helps developers understand how to interact with different resources.
GET
Use GET to retrieve resources without modifying existing data.
POST
Use POST to create a new resource or submit data for processing.
PUT
Use PUT when replacing an existing resource with a new representation.
PATCH
Use PATCH when updating specific fields or parts of an existing resource.
DELETE
Use DELETE to remove a resource.
Example:
GET    /users
POST   /users
PUT    /users/101
PATCH  /users/101
DELETE /users/101
Using HTTP methods consistently creates a predictable API structure and reduces integration confusion.
Maintain Consistent Naming Conventions
Consistency in naming makes APIs easier to understand, use, and maintain. Developers should establish naming standards before creating endpoints and apply them across the entire API.
URL and Endpoint Naming
Keep endpoint names simple and consistent. Use a common format for resources, pluralization, capitalization, and nested relationships.
/users
/users/101/orders
/products
Request and Response Field Naming
Request and response fields should also follow a consistent naming style. For example, an API can consistently use first_name and last_name or firstName and lastName rather than mixing different conventions.
Example:
{
"userId": 101,
"firstName": "John",
"lastName": "Smith"
}
A consistent naming strategy makes API responses more predictable and reduces unnecessary development effort.
Use Appropriate HTTP Status Codes
HTTP status codes give clients immediate information about whether a request succeeded or encountered an issue. Choosing the appropriate status code makes API behavior easier to understand and troubleshoot.
Successful Responses
Common success codes include:
- 200 OK – The request was successfully processed.
- 201 Created – A new resource was successfully created.
- 204 No Content – The request succeeded without returning a response body.
Client Errors
Client-side issues can be represented with codes such as:
- 400 Bad Request – The request contains invalid or missing information.
- 401 Unauthorized – Authentication is required or invalid.
- 403 Forbidden – The client does not have permission to access the resource.
- 404 Not Found – The requested resource does not exist.
Server Errors
Use 500 Internal Server Error for unexpected problems occurring on the server. Use other 5xx status codes when a more specific server-side condition applies.
Example:
POST /users
→ 201 Created
GET /users/999
→ 404 Not Found
Using meaningful status codes allows consuming applications to handle responses appropriately.
Keep API Design Simple and Intuitive
An API should let developers understand its behavior without studying complicated rules. Simplicity improves usability and reduces the learning curve for developers integrating with the API.
Avoid Unnecessary Complexity
Avoid excessive parameters, deeply nested endpoints, and redundant functionality. Each endpoint should have a clear purpose and provide only the information required for the intended operation.
Maintain Predictable API Behavior
Similar operations should behave in similar ways throughout the API. Consistent request structures, response formats, and endpoint patterns make APIs easier to consume and maintain.
Example:
Instead of creating separate endpoints for every possible action, use resource-oriented endpoints with appropriate HTTP methods:
GET    /orders/101
PATCH  /orders/101
DELETE /orders/101
This keeps the API structure straightforward and easier to extend.
Design for Security
Consider security throughout the API lifecycle, not only after development. APIs often handle sensitive business and user data, making proper protection essential. Following API security practices can help protect endpoints, user data, and backend resources from common threats.
Authentication and Authorization
Use secure authentication mechanisms to verify API users or applications. Authorization should then determine which resources and operations each authenticated client can access.
Data Validation
Validate incoming data before processing it. Input validation helps prevent malformed API requests and reduces the risk of common security issues.
Rate Limiting
Rate limiting controls how many requests a client can make within a specific period. It can help protect APIs from excessive traffic, abuse, and resource exhaustion.
Example:
POST /users
Authorization: Bearer
{
"email": "user@example.com",
"name": "John Smith"
}
Sensitive information should also be transmitted over secure connections and handled according to applicable security requirements.
Implement API Versioning
As applications evolve, APIs may need changes that could affect existing consumers. API versioning provides a structured way to introduce changes while maintaining compatibility with older integrations.
URL Versioning
Version information can be included directly in the endpoint:
/api/v1/users
/api/v2/users
This approach is simple and makes the API version immediately visible.
Header Versioning
Another approach is to specify the API version through request headers. This keeps version information out of the URL while allowing clients to request a particular API version.
Example:
GET /users
Accept: application/vnd.company.v2+json
Whichever approach you choose, apply versioning consistently and support it with a clear migration strategy.
Provide Consistent Error Handling
Well-structured error responses help developers quickly identify and resolve problems. Instead of returning different error formats across endpoints, APIs should use a standardized structure.
Standard Error Response Structure
A consistent response can include an error code, message, and additional details where appropriate.
{
"error": {
"code": "INVALID_EMAIL",
"message": "The provided email address is invalid."
}
}
Meaningful Error Messages
Error messages should explain what went wrong without exposing sensitive internal information. Clear messages help API consumers understand how to correct invalid requests.
Support Filtering, Sorting, and Pagination
APIs that return large datasets can become inefficient if they send every available record in a single response. Filtering, sorting, and pagination give clients greater control over the data they receive.
Filtering
Filtering lets clients request only records that match specific criteria.
GET /products?category=electronics
Sorting
Sorting lets clients control the order of returned results.
GET /products?sort=price
Pagination
Pagination divides large datasets into smaller, manageable responses.
GET /products?page=2&limit=20These capabilities can reduce unnecessary data transfer and improve the overall efficiency of API interactions.
Create Clear API Documentation
Good documentation is essential for helping developers understand how to integrate with an API. Even a technically well-designed API can be hard to use if its behavior and requirements aren’t clearly documented.
Endpoint Documentation
Document each API endpoint along with its purpose, HTTP method, URL structure, query parameters, and expected responses.
Request and Response Examples
Include practical examples showing how requests should be structured and what clients can expect in return.
{
"id": 101,
"name": "Wireless Headphones",
"price": 99.99
}
Authentication Instructions
Clearly explain the authentication method, required headers, token format, and relevant permissions. Well-maintained documentation helps developers integrate faster and reduces unnecessary support requests.
Example:
A complete endpoint reference could include:
GET /api/v1/products/{id}
Authentication: Bearer Token
Response: 200 OK
{
"id": 101,
"name": "Wireless Headphones",
"price": 99.99
}
Clear, up-to-date documentation makes an API easier to adopt, test, and maintain throughout its lifecycle.
You May Also Like:
API Design Best Practices
A well-designed API is easy to understand, reliable, secure, and efficient. Following established API design practices helps developers integrate with your services faster while reducing maintenance costs and compatibility issues:
Follow Consistent API Standards
Consistency makes APIs easier to learn and use. Follow a clear naming convention for endpoints, parameters, HTTP methods, status codes, and response formats. For REST APIs, use standard HTTP methods such as GET, POST, PUT, PATCH, and DELETE appropriately. Maintain a predictable URL structure and return consistent error responses across the API.
Design With Developers in Mind
An API should be intuitive for the developers who consume it. Use meaningful endpoint and field names, provide clear documentation, and include practical examples. Avoid unnecessary complexity and make common operations straightforward. Good API documentation should explain authentication, request and response formats, errors, rate limits, and usage examples.
Prioritize Backward Compatibility
API changes should not unexpectedly break existing applications. Avoid removing or renaming existing fields and endpoints without a proper migration strategy. When breaking changes are unavoidable, use API versioning and give developers enough notice and documentation to migrate. Backward compatibility builds trust and reduces integration problems.
Optimize API Performance
API performance directly affects the user experience of applications that depend on your services. Minimize unnecessary database queries and network requests, use caching where appropriate, and return only the data clients need. Use pagination for large datasets, and use techniques such as compression and asynchronous processing to improve response times for larger operations.
Test APIs Continuously
Continuous testing helps identify defects before they affect users. Create automated tests for individual endpoints, authentication, validation, error handling, and integration scenarios. Include regression tests whenever you introduce new functionality or make changes. Running API tests as part of the CI/CD pipeline helps maintain reliability throughout the development lifecycle.
Monitor and Improve APIs After Deployment
API development does not end when an API is released. As part of the API development lifecycle, monitor response times, error rates, availability, traffic patterns, and resource usage in production. Logging and observability tools can help identify issues and understand how developers use the API. Use these insights to improve performance, reliability, documentation, and future API versions.
How Does Moon Technolabs Help Build Well-designed and Scalable APIs?
Moon Technolabs helps businesses build well-designed APIs that are secure, flexible, and easy to integrate with web and mobile applications. Our development approach focuses on clean architecture, efficient data handling, strong security, and clear documentation to ensure reliable performance.
Our team designs scalable APIs that can support growing users, data, and application requirements while maintaining optimal performance. With the right custom API development partner, businesses can build high-performing APIs tailored to their unique products, workflows, and integration needs.
Stop Rewriting Code and Ship Scalable APIs Faster
Cut development time in half with proven architectural patterns, clean design principles, and expert guidance from seasoned system engineers.
Conclusion
Following the right REST API design principles lays a strong foundation for applications that are secure, dependable, and ready to scale. By focusing on consistency, performance, security, documentation, and flexibility, businesses can build APIs that keep delivering value as their products and user base evolve.
For organizations building API-driven digital products, choosing the right development partner can make the implementation process more efficient. As a proficient full-stack development company, we can bring API architecture, application logic, and user-facing experiences together to create a connected and future-ready solution.
FAQs
01
What are the most important API design principles?
Key principles include maintaining statelessness, ensuring resource-oriented URL structures, using correct HTTP methods (GET, POST, PUT, DELETE), returning meaningful status codes, prioritizing robust security, maintaining consistency, and providing clear documentation for developers.02
What is the difference between API design principles and API design patterns?
Principles are high-level, abstract guidelines informing quality and general rules (like consistency or simplicity). Patterns are concrete, reusable, low-level architectural solutions or templates that address recurring structural programming problems in specific contexts.03
Why is consistency important in API design?
Consistency minimizes developer friction and follows the principle of least astonishment. Uniform naming conventions, predictable error handling, and standard status codes make endpoints intuitive, reducing learning curves, integration errors, and ongoing debugging time.04
How do you design APIs for scalability?
Scalability involves keeping servers stateless so you can distribute requests horizontally, implementing efficient caching strategies, using pagination for large datasets, compressing payloads, and applying rate limiting to manage high API traffic and prevent performance degradation.05
How much does custom API design and development cost?
Custom API development typically ranges from $5,000 to $20,000+ for basic-to-moderate projects. Enterprise-grade systems with advanced security, documentation, and complex integrations can exceed $50,000, depending heavily on developer rates and project scope.


The Software Development Team at Moon Technolabs includes experienced developers, solution architects, and technology consultants who contribute content on software engineering, application development, system architecture, and digital innovation. Their articles are based on real-world project experience and aim to help businesses make informed technology decisions.
Submitting the form below will ensure a prompt response from us.
We refine our expertise to deliver innovative business solutions.

205 N Michigan Avenue, #810, Chicago, 60601, Illinois, United States
13500 Long Is Dr, Pflugerville, TX 78660, USA

C/105 Ganesh Meridian, S.G. Highway, Ahmedabad, GJ 380060



Ayse D.
Co-Founder France
“ I highly recommend Moon Technolabs as the quality of service is wonderful. We have hired this company to develop the product based on some complex & technical issues. We get the best quality services as compared with others in the market. Huge Thanks to Moon Technolabs as the team is always ready to give the solution all time.”

Justin G.
Founder & CEO USA
“ Moon Technolabs is a pioneer in the WebRTC based project as they have fixed complicated segments of the module by fulfilling different product lines by providing 24X7 customer support. We really recommended Moon Technolabs as they are able to develop products as per the module deadline and project timeline.”

Flavio S.
Founder & Managing Director Germany
“I am happy to recommend Moon Technolabs for their app development services. They successfully developed apps for me, and I am highly satisfied with the overall outcomes. The development team has swiftly addressed the issues with responsive and effective communication to understand the requirement quickly and actively resolve the back-and-forth problems that arose...”

Jay M.
Founder & CEOUSA“Moon Technolabs is the best company that provides advanced apps and websites development services in the USA and Europe. I am a newbie to develop my app with an external team. I am really happy to work with them as I am not that much mobile apps user. Here, the team and specially the CEO of Moon Technolabs helps me to let me know about the benefits of my app to generate revenue....”


Our Offices
India
C/105 Ganesh Meridian,S.G. Highway, Ahmedabad, GJ 380060USA
205 N Michigan Avenue, #810, Chicago, 60601, Illinois, United StatesContact Information


